Privacy & security
Is a Temp Mail Link Safe? How to Inspect Before Clicking
Opening an email in FreeTemp is sandboxed, but clicking a temp mail link leaves the sandbox. See what FreeTemp blocks and 5 checks before you click.
By FreeTemp7 min read
Opening and reading a message inside FreeTemp is protected by HTML sanitization and a scriptless sandboxed frame, but clicking a temp mail link opens an external website in a new browser tab outside FreeTemp's protection. FreeTemp neutralizes dangerous javascript: schemes, strips fake HTML forms, blocks tracking pixels, and prints each extracted link's destination hostname in parentheses so you can inspect it first. Whether a link is safe to click ultimately depends on verifying that you requested the email yourself and that the destination domain truly belongs to the service you just used.
Two Separate Security Zones: Inside the Preview vs After You Click
Many users worry that merely viewing a suspicious message in a web inbox could infect their browser, while others make the opposite mistake—assuming that because an email arrived inside a clean interface, every button inside it must be trustworthy. Separating what happens inside FreeTemp from what happens after a click makes the real risk crystal clear.
Zone 1: What FreeTemp Neutralizes Automatically Before You Click
Every incoming message passes through a multi-layer defense verified in FreeTemp's parser and front-end message viewer:
| Built-In Protection Layer | Exact Implementation in FreeTemp | Threat It Eliminates |
|---|---|---|
| HTML & tag sanitization | DOMPurify strips <script>, <iframe>, <object>, <embed>, <form>, <input>, <meta>, <base>, and inline handlers (onclick, onerror) | Cross-site scripting (XSS) and embedded fake login forms inside the email body |
Scriptless sandboxed iframe | Renders with sandbox="allow-popups allow-popups-to-escape-sandbox" (no allow-scripts, no allow-same-origin) | Prevents email content from executing code or reading your localStorage mailbox token |
| Strict Content Security Policy | default-src 'none'; img-src data:; font-src 'none'; form-action 'none' + CSS url() removal | Blocks remote tracking pixels, external fonts, and silent background network requests |
| Protocol & referrer isolation | Only http: / https: links pass extraction; every link carries rel="noopener noreferrer nofollow" and no-referrer | Blocks javascript: / data: URI exploits and hides your FreeTemp URL from the target server |
| Smart hostname badge (first 60 KB) | Extracts up to 5 top verification links and displays (url.hostname) in plain text next to the button | Exposes deceptive anchor text where a button says one brand name but points elsewhere |
Zone 2: What Happens the Moment You Click an External Link
To let legitimate account activation work, links open in a new browser tab outside the sandbox. From that split second onward, your browser talks directly to the remote web server. FreeTemp cannot inspect what loads on that external page, stop a lookalike phishing site from asking for a password or payment card, unmask a third-party click-tracking redirect before your browser follows it, or scan a file you download there for malware. Read the broader privacy model in is temporary email safe and what it protects.
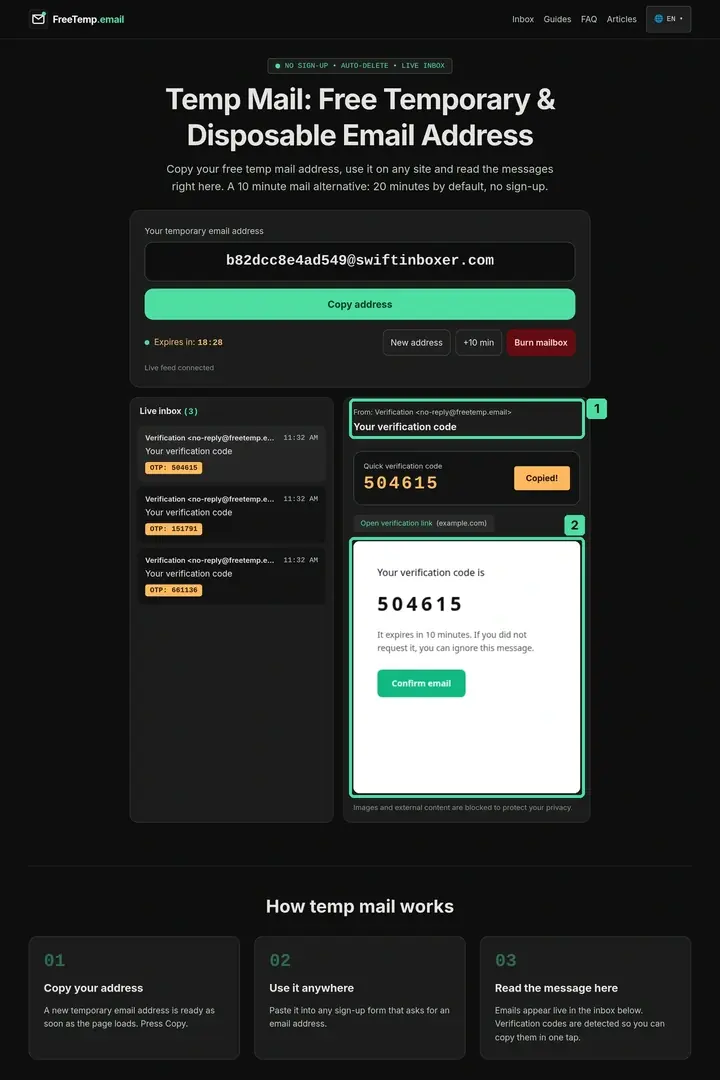
Five-Step Checklist Before Clicking Any Temp Mail Link
Whenever a confirmation message lands in your FreeTemp live inbox, spend five seconds running these checks in order:
- Confirm you triggered this exact email moments ago: Because your address was just created for a 20-minute session, only the website you just submitted should be emailing you. If an unexpected "prize notification," "invoice alert," or "account suspension" arrives unsolicited, never click anything—burn the mailbox immediately.
- Match the sender header to the website open in your other tab: Look at the
Fromaddress and subject line above the preview. Watch out for subtle character swaps (such asrnpretending to bem, extra hyphens, or unrelated free webmail senders). - Read the hostname in parentheses on the extracted link badge: Above the message body, FreeTemp lists up to five extracted links with their exact parsed hostname—for example,
Verify link (example.com). Verify that the root domain (the label right before.com,.org,.io, etc.) matches the site you signed up on, or follow the visual walkthrough in how to open a confirmation link safely. - Prefer a 6-digit OTP code whenever the email offers both: Many services include both a "Confirm Email" button and a numeric code in the same message. Copying the digits into the tab you already opened yourself avoids following external links altogether—see how to receive verification codes without personal email.
- Inspect the browser address bar again after the new tab loads: Legitimate companies sometimes route activation links through mail delivery providers (like
sendgrid.netoramazonses.com) that immediately redirect to their real domain. Wait for the page to finish loading and confirm the final HTTPS URL in your browser's address bar matches the real site before typing anything.
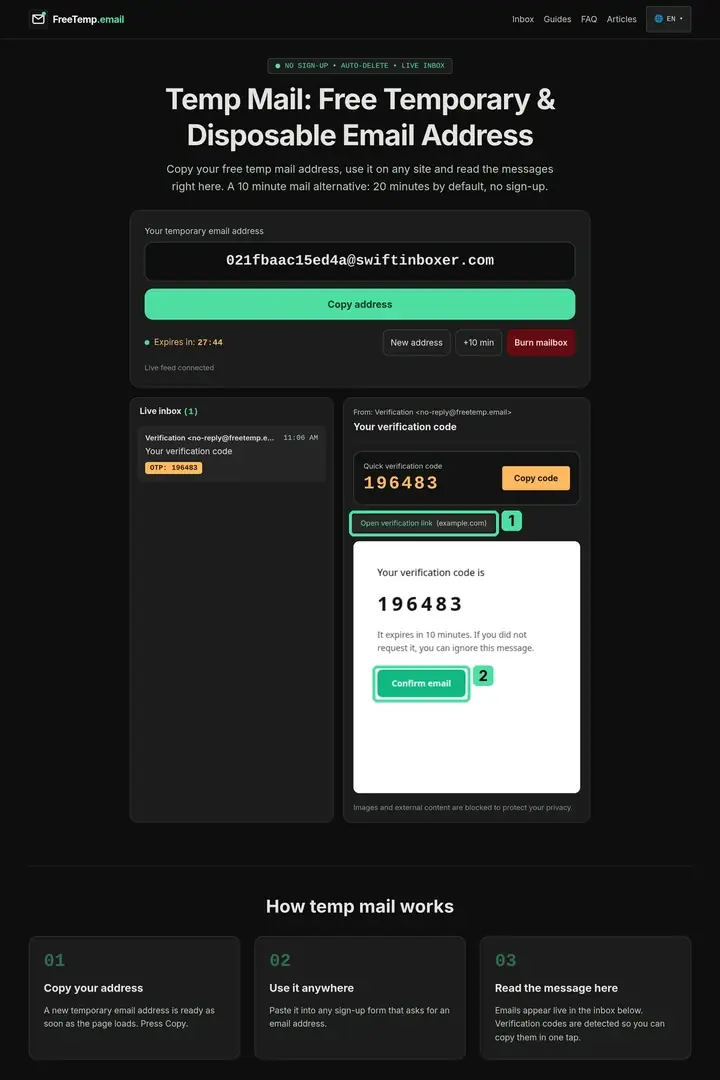
Worked Example: Comparing a Legitimate Redirect Against a Lookalike Trap
Suppose a QA tester uses one temporary address to register on acme-analytics.io for a sandbox demo, and two messages arrive within a minute:
- Message A (Expected signup confirmation): Sent from
no-reply@acme-analytics.ioforty seconds after submitting the form. The extracted badge readsVerify link (auth.acme-analytics.io). Clicking openshttps://auth.acme-analytics.io/confirm?token=...over HTTPS, displays "Email verified!", and asks for nothing else. Totally normal. - Message B (Follow-up promotional partner offer): Sent from an unfamiliar marketing domain with a shiny HTML button labeled "Download Your Bonus Toolkit." Even though the button text looks friendly, FreeTemp's hostname badge reveals
(files-drop-mirror.info)—a domain the tester never visited. When the new tab asks to download a password-protected.ziparchive, the tester closes the tab immediately and burns the mailbox. Compare how promotional partner lists spread in how to avoid spam with a temporary email address.
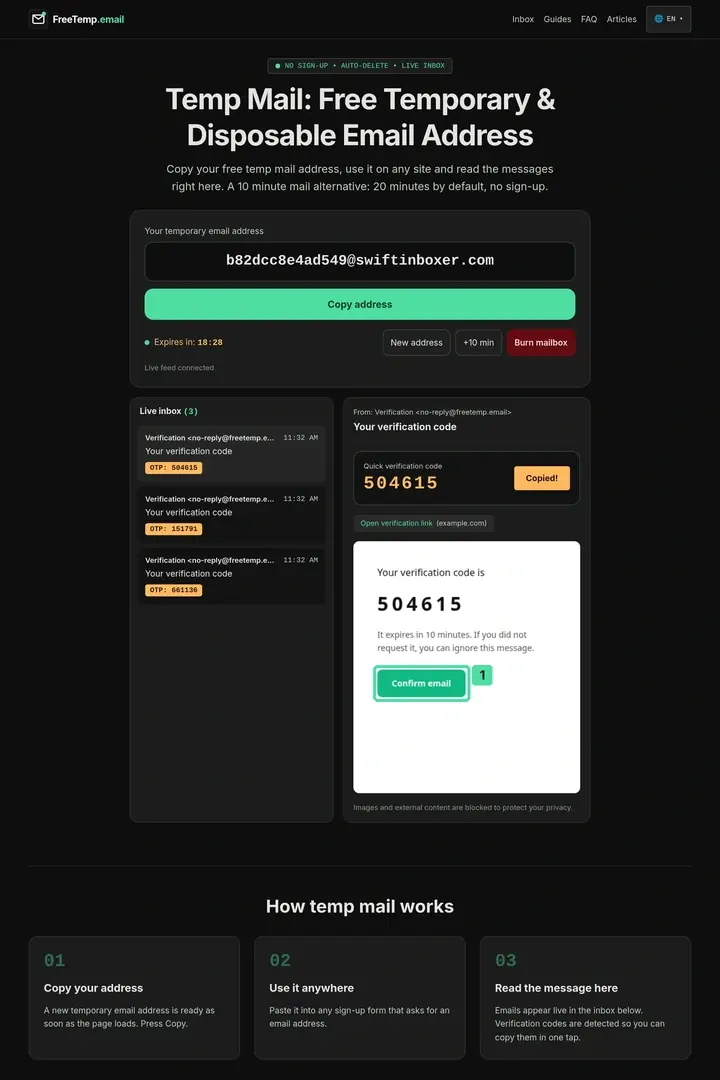
Common Mistakes Users Make With Email Confirmation Links
- Trusting the blue button label instead of the actual hostname: Senders can write any text—even a full
https://trusted-site.comURL—as the visible label of an<a>tag while pointinghrefsomewhere else. Always check FreeTemp's parenthesized hostname badge or your browser's hover preview. - Clicking "Unsubscribe" links on unsolicited junk messages: You do not need to unsubscribe a 20-minute inbox; pressing Burn mailbox deletes the entire address cleanly without signaling to a dubious sender that you clicked.
- Looking for links at the very bottom of a massive 200 KB newsletter in the top badge bar: FreeTemp's automatic link extractor scans the first 60 KB and displays up to 5 prioritized action links; for valid links further down a long message, inspect them directly inside the sanitized preview.
- Downloading archive files from unknown hosts: Remember FreeTemp strips email attachments by design, so attackers often replace attachments with external file-sharing links. Never run untrusted downloads just because they arrived during a test signup.
Verify the Domain, Finish the Task, and Burn the Box
FreeTemp handles the heavy lifting inside the inbox—stripping scripts, blocking tracking pixels, isolating HTML inside a zero-privilege frame, and exposing the real hostname of extracted links. Pair those technical guardrails with a five-second domain check before you click, prefer numeric OTP codes whenever offered, and burn the mailbox the moment your confirmation succeeds.
Frequently asked questions
Can simply opening a suspicious email inside FreeTemp infect my device without clicking any link?
FreeTemp strips scripts, forms, embeds, and event attributes with DOMPurify and displays the message inside a sandboxed iframe with JavaScript and external resources disabled. While keeping your browser updated is always wise, passive viewing inside the isolated preview blocks standard script and tracking-pixel attacks.
Why does the domain in parentheses next to a confirmation link say sendgrid.net or list-manage.com instead of the website name?
Many legitimate websites send transactional mail through cloud email providers that wrap links in click-tracking domains before redirecting to the real website. Only click if you just requested the email yourself, and verify the final URL in your browser’s address bar as soon as the page loads.
Does the external website see my FreeTemp inbox address from browser referrer headers when I click a link?
No. FreeTemp sets referrerPolicy="no-referrer" on the preview frame and adds rel="noopener noreferrer nofollow" to every link. However, the website’s own unique confirmation token in the URL naturally tells that specific website which signup is being confirmed.
Why did FreeTemp only show five links at the top when the email contains twelve?
FreeTemp scans the first 60 KB of the message, ranks verification and login URLs ahead of footer and unsubscribe links, and displays up to five top http/https links as quick badges so the header stays uncluttered. All remaining sanitized links remain visible inside the message preview.