Verification & sign-up
Temporary Email for Verification: Get Codes Privately
Use a temporary email for verification to receive one-time codes without exposing your personal inbox. Step-by-step workflow, timing tips, and fixes.
By FreeTemp7 min read
Using a temporary email for verification lets you receive a one-time passcode (OTP) in a live browser inbox while keeping your personal email address off unfamiliar mailing lists. You copy the disposable address into the signup or download form, read the 4-to-8-digit code as soon as it lands over WebSocket, and complete verification in seconds. Once the session expires or you burn the inbox, no trace of the message remains in your personal mail.
Step-by-Step: Using Temporary Email for Verification
One-time passcodes are strict about both accuracy and timing—most senders invalidate a code within 3 to 10 minutes, or immediately if a second code is requested. Following a clean sequence prevents expired codes and clipboard mix-ups:
- Open the FreeTemp live inbox in its own browser tab before clicking the signup or download button on the other website.
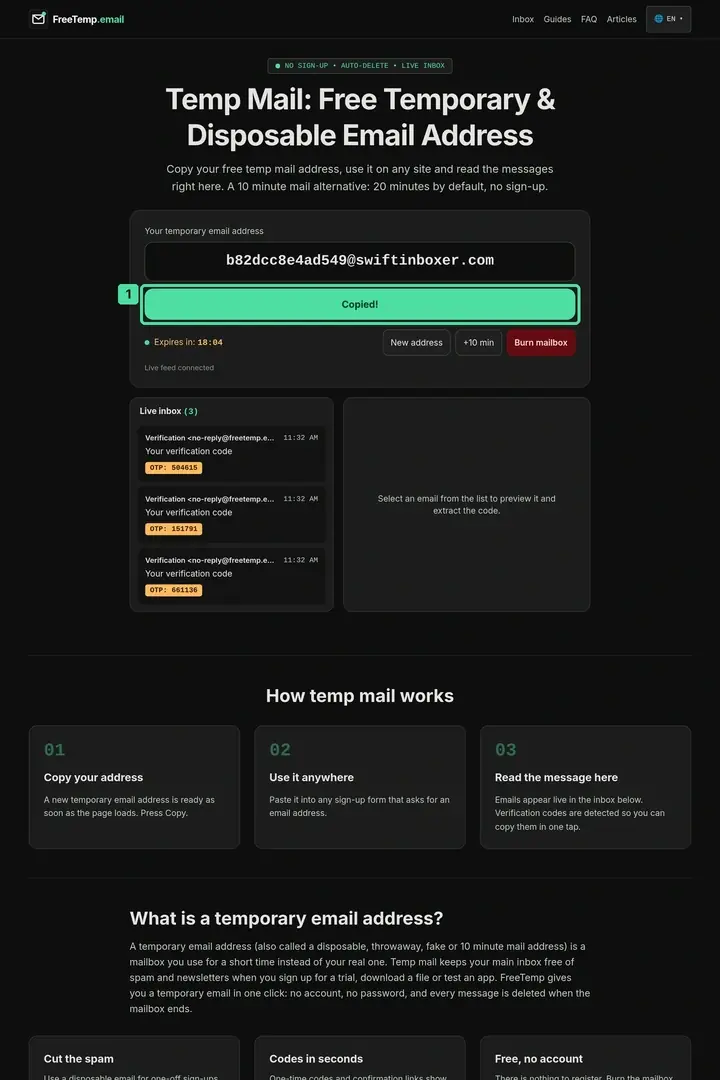
- Complete the brief bot check if shown, then press Copy address and wait for the button label to change to Copied!.
- Switch to the target website, paste the full address into the email field, verify there are no leading or trailing spaces, and submit the form once.
- Return to your FreeTemp tab and watch the live inbox—do not reload the page or click New address.
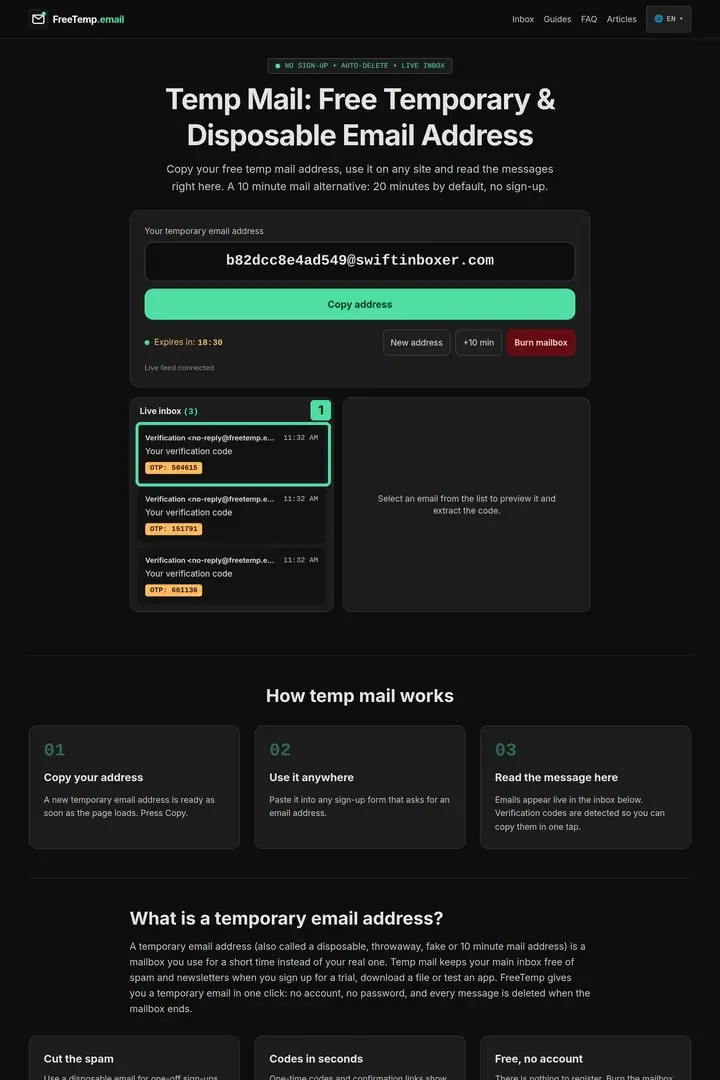
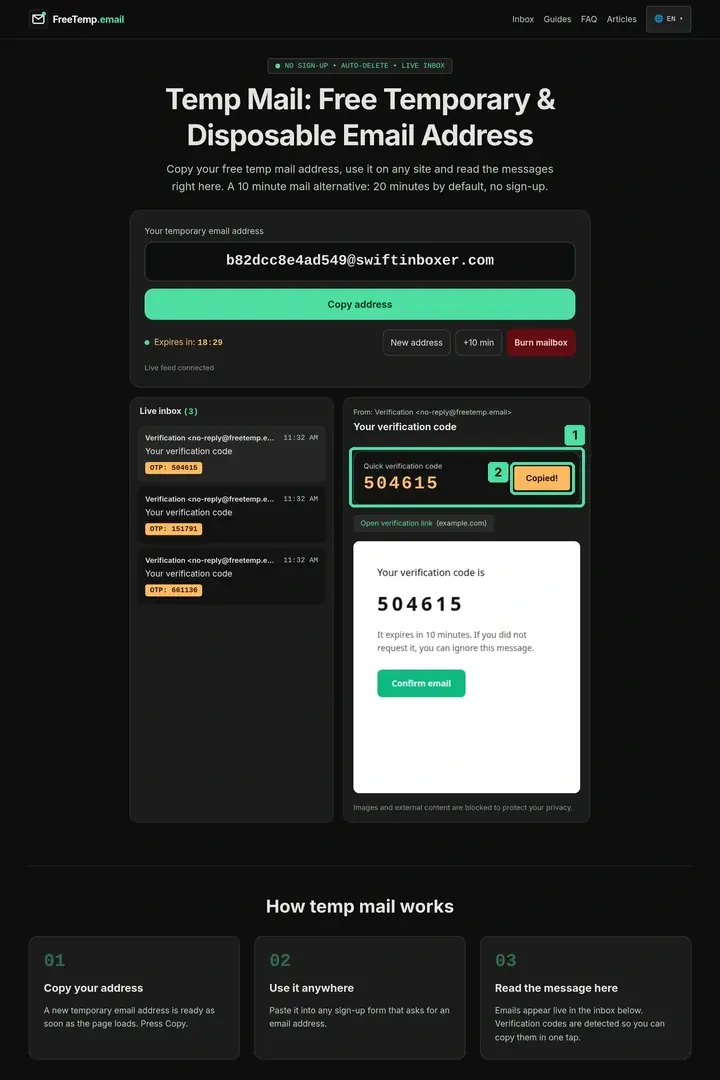
- Click the arrived verification message at the top of the list; if FreeTemp detects an OTP, press Copy code on the quick-code card.
- Paste the digits into the website's verification prompt, confirm completion, and optionally press Burn mailbox when finished.
How FreeTemp Extracts One-Time Codes and Confirmation Links
Searching through dense HTML templates on a small phone screen is where many users copy the wrong digits—such as a street number in the email footer or a CSS color value. FreeTemp's streaming mail parser scans the first 60 KB of incoming plain text and cleaned HTML to surface the actionable part automatically.
What the Quick Verification Code Card Detects
When an email arrives, the parser looks for standard verification patterns in both English and Arabic—such as phrases like "verification code," "security code," "OTP," or "passcode" followed or preceded by a 4-to-8-character code, prefixed strings like G-123456, or hyphenated groups like 482-910. To avoid false positives, it strips out hexadecimal colors (#4edea3), clock timestamps (14:30), and CSS pixel sizes before highlighting standalone 4-to-8-digit numbers.
Handling Magic Links and Unusual Code Formats
Not every service sends digits; some send a "Confirm email" button, while others embed codes inside custom phrasing or split digits across separate HTML cells. Compare how FreeTemp handles each format so you never get stuck waiting for a card that will not appear:
| Verification Format Sent by Website | What You See in FreeTemp | Fastest Action to Take |
|---|---|---|
| Standard 4–8 digit numeric OTP | Orange tag in inbox row + Quick verification code card | Press Copy code on the card and paste immediately |
Hyphenated or prefixed code (391-842) | Extracted on the Quick verification code card | Copy from the card; check whether the form expects the hyphen |
| Confirmation or activation URL | Extracted link button showing destination domain in brackets | Verify the bracketed domain matches the site, then follow how to open a confirmation link safely |
| Unusual alphanumeric string in body text | Full message rendered inside the isolated preview | Open the message row and highlight the code directly from the text |
| Code embedded inside a remote image | Remote image blocked by default for privacy | External image-only codes cannot load; use a standard alias if required |
Worked Example: Verifying a One-Off API Sandbox Documentation Portal
Imagine you are evaluating an open-data weather API whose interactive documentation requires email verification before showing sample response schemas, and you want to inspect the docs without adding your work inbox to a vendor newsletter.
At 10:00, you open FreeTemp; the countdown starts at 20:00 and displays a fresh address. At 10:01, you copy the address, paste it into the documentation portal's email prompt, and press "Send code." You switch back to the FreeTemp tab without refreshing. At 10:01:14, the WebSocket connection pushes the new message into row 1 with an extracted 6-digit code on the quick-code card. You click Copy code, switch tabs, paste the six digits at 10:01:25, and unlock the documentation page—all in under ninety seconds, with zero exposure of your personal or company email.
Managing Code Expiry and Mobile Browser Tabs
Two separate clocks run during every verification flow: the target website's OTP validity clock (often 2 to 10 minutes) and FreeTemp's server-side inbox timer (20 minutes by default, extendable in +10 minute steps up to 60 minutes). Keeping both clocks aligned eliminates almost all failed attempts.
Extending Before Slow Senders Time Out
Some enterprise mail gateways batch outbound verification emails or pass through greylisting delays of one to three minutes. If your FreeTemp timer is already below five minutes before you submit a form, press +10 min first so the mailbox cannot expire while the message is queued in transit.
Switching Between Apps on Android and iPhone
On phones, switching from your browser to another app can put the background browser tab to sleep, pausing its live WebSocket temporarily. When you switch back to the same browser tab, FreeTemp reads your saved session from localStorage and syncs arrived messages—so avoid swiping the tab closed or using private mode if you need to jump between apps. For mobile-specific details, see the step-by-step guide to receiving a verification code.
Common Mistakes That Invalidate Verification Codes
Even when the email arrives in two seconds, small workflow slips can cause the website to reject the digits you paste:
- Pressing "Resend code" repeatedly: Clicking resend three times in thirty seconds usually invalidates the first two codes on the sender's server. If three emails arrive, ignore the bottom two rows and copy only from the newest message at the very top.
- Confusing "Copy address" with "Copy code": The top bar copies your email address, while the card inside the opened message copies the numeric OTP. Pasting an email address into a 6-digit input box silently truncates or fails validation.
- Mobile keyboard auto-spacing: Some phone keyboards append a trailing space after pasting into a text field, turning a 6-character code into 7 characters. Check the cursor position before pressing submit.
- Waiting blindly when a domain is filtered: If two minutes pass after a clean paste and a single resend still delivers nothing, walk through fixes when a verification email is not arriving or check why a website rejects temporary email domains rather than requesting ten more codes.
Deciding Whether Temporary Verification Fits Your Task
Before pasting a disposable address into any verification prompt, ask whether you will need that login next week. For one-time downloads, public Wi-Fi gates, and developer testing, a short-lived inbox keeps your real address private and spam-free. Whenever an account stores your work, purchases, or security settings, verify it with a permanent mailbox or a forwarding alias under your long-term control.
Frequently asked questions
Why did my email arrive without showing the Quick verification code card?
Some senders format passcodes in unusual ways—such as spacing every digit apart or phrasing the sentence without standard verification keywords. Simply click the arrived message row to read and copy the code directly from the isolated text preview.
What should I do if two verification emails arrive and the code says invalid?
Requesting a second code almost always cancels the first one on the website server. Check the arrival time in your FreeTemp inbox list, open the top-most (newest) message, and enter only that latest code.
Can I reuse the same FreeTemp address tomorrow if the website asks to verify again?
No. Every FreeTemp inbox expires permanently after its 20-minute default timer (or up to 60 minutes if extended). If a website may ask for email verification on future logins, use a permanent email or forwarding alias instead.
Does copying the code from FreeTemp let the sender track me?
No. Copying from the quick-code card happens locally in your browser, and FreeTemp blocks external tracking images inside the message preview by default so opening the message does not trigger remote open-tracking pixels.